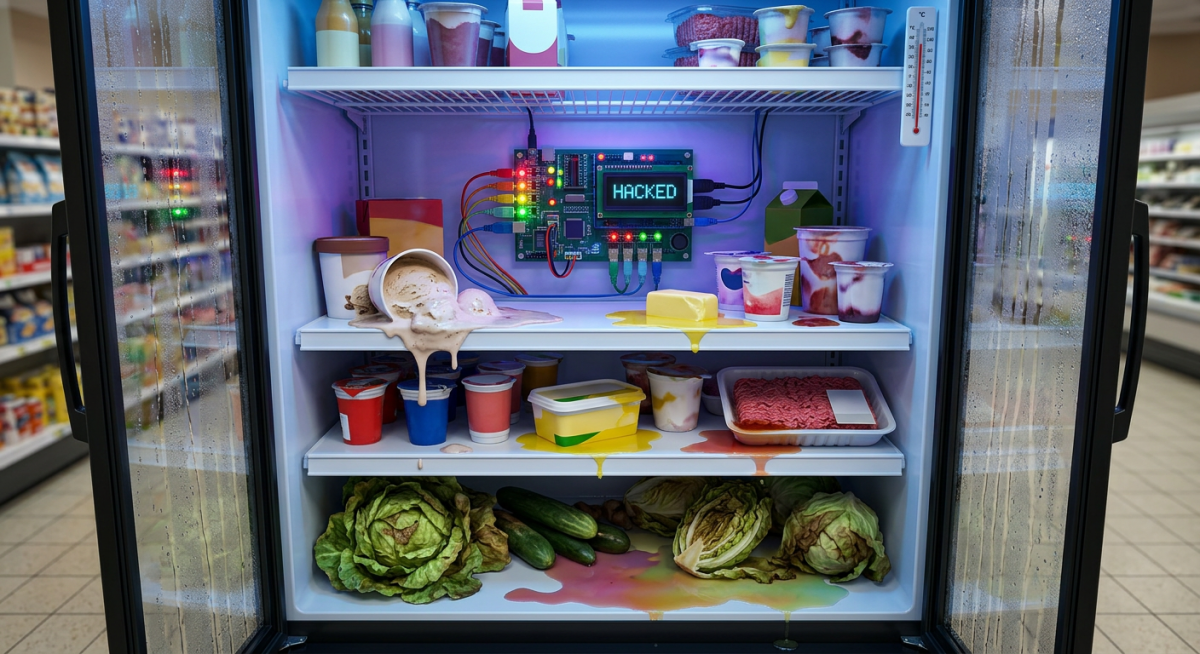
The newsworthy attack on refrigeration systems in France appears, at the time of writing, to have involved internet-connected refrigeration controllers running outdated software, including equipment that is now end-of-life.
Once the attackers had access, they were able to manipulate the refrigeration controls, reportedly forcing systems into continuous defrost cycles and pushing temperatures towards 50°C. The result was spoiled food, damaged equipment and, in some locations, reports of fires.
And this is where Operational Technology (OT) worries me.
A compromised corporate system can result in lost data, ransomware or disruption.
A compromised OT system can have real-world, physical consequences.
The remote access presumably exists for a perfectly sensible reason: refrigeration engineers need to maintain these systems without travelling to every site.
But we appear to be learning the same security lessons again and again:
Change the default passwords.
Patch the devices.
Don’t expose management interfaces directly to the internet.
Don’t allow remote access from locations that have no reason to access them.
This has been demonstrated previously: https://lnkd.in/p/ewQ77-72
My own rather less dramatic example happened this week.
I woke up to find a login attempt against one of my cloud accounts from Rajasthan at around 3am.
Fortunately, some time ago I’d enabled MFA.
It’s not a panacea, but in this instance one very basic security control removed most of the worry and potential heartache of someone taking over the account.
So perhaps the strategic security plan for an organisation of almost any size doesn’t need to start with another shiny product.
Start with:
- Audit everything connected to the internet corporate, OT and BMS.
- Establish what remote access each device actually requires.
- Only permit that access.
- Use MFA wherever it is supported, particularly at remote-access boundaries.
- Put third-party maintenance access behind a bastion/jump host.
- Make use of that controlled path mandatory if you don’t use it, you don’t connect.
- And most importantly: make somebody responsible for all of the above.
None of this is particularly exciting.
None of it is new.
But attackers don’t get extra points for sophistication.
If the basics give them a way in, they’ll use the basics.